Cybersecurity Alert: Major Healthcare Data Breach Affects Over 5 Million Patients in Early 2026, New Regulations Expected
The digital landscape of healthcare, while offering unprecedented advancements in patient care and operational efficiency, also presents an ever-expanding attack surface for malicious actors. In a stark reminder of these vulnerabilities, early 2026 witnessed a catastrophic healthcare data breach, compromising the sensitive personal and medical information of over 5 million patients. This incident has sent shockwaves through the industry, prompting urgent calls for enhanced cybersecurity measures and foreshadowing the imminent introduction of more stringent regulations.
This article delves into the specifics of this major security lapse, exploring its profound implications for patients, healthcare providers, and the broader digital health ecosystem. We will analyze the nature of the compromised data, the potential fallout for affected individuals, and the critical lessons that must be learned. Furthermore, we will examine the anticipated regulatory responses, discussing how these new frameworks aim to fortify defenses against future cyber threats and restore public trust in the security of health information.
Understanding the Scope of the 2026 Healthcare Data Breach
The recent healthcare data breach, identified in the first quarter of 2026, was a sophisticated attack targeting a prominent network of healthcare providers and their associated third-party vendors. Initial reports indicate that the breach originated through a supply chain vulnerability, a common vector for cyberattacks in recent years. Threat actors exploited a weakness in a widely used patient management software, gaining unauthorized access to databases containing a wealth of protected health information (PHI).
The compromised data is extensive, including, but not limited to: full names, addresses, dates of birth, social security numbers, insurance policy information, medical record numbers, diagnostic codes, treatment histories, and in some cases, even financial details. The sheer volume and sensitivity of this data make this particular healthcare data breach one of the most significant in recent memory, surpassing many previous incidents in both scale and potential impact.
Forensic investigations are ongoing, but preliminary findings suggest that the attackers maintained access to the systems for several weeks before detection. This prolonged access allowed them to exfiltrate a vast amount of data, raising concerns about the potential for identity theft, medical fraud, and targeted phishing campaigns against affected individuals. The incident underscores the critical need for robust, multi-layered security strategies that extend beyond an organization’s immediate perimeter to encompass its entire vendor ecosystem.
Immediate Repercussions for Patients and Providers
The fallout from such a massive healthcare data breach is multifaceted and severe. For the over 5 million affected patients, the immediate concern is the risk of identity theft and financial fraud. Criminals can leverage stolen social security numbers and personal details to open fraudulent accounts, file false tax returns, or even commit medical identity theft, where an individual’s stolen information is used to obtain medical services or prescription drugs.
Beyond financial risks, patients also face a significant invasion of privacy. The exposure of sensitive medical histories can lead to discrimination, social stigma, and emotional distress. For example, information about mental health conditions, chronic illnesses, or sensitive treatments could be used maliciously, causing profound personal harm.
Healthcare providers, too, face immense challenges. The affected organizations are grappling with significant financial penalties, including potential fines under existing regulations like HIPAA, as well as the substantial costs associated with incident response, forensic investigations, legal fees, and credit monitoring services for affected individuals. Furthermore, the reputational damage can be immense, leading to a loss of patient trust and a potential decline in patient enrollment. The incident has also placed considerable strain on IT departments, who are working around the clock to patch vulnerabilities, enhance security protocols, and comply with reporting requirements.
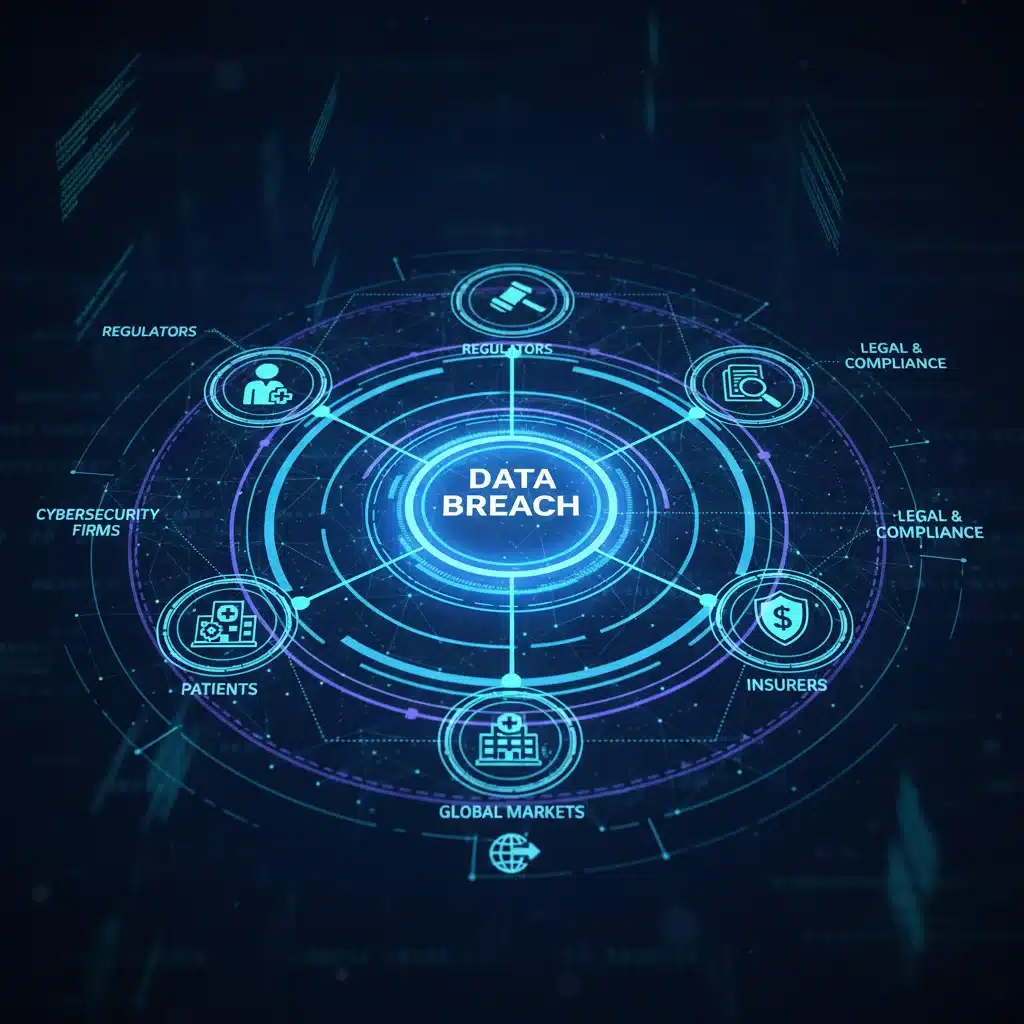
The ripple effect extends to the broader healthcare system, as other providers and insurers are now re-evaluating their own security postures, realizing that a breach at one entity can have systemic consequences. The interconnected nature of modern healthcare means that a vulnerability anywhere can become a threat everywhere.
The Regulatory Landscape Before the Breach: HIPAA and Its Limitations
Prior to this 2026 healthcare data breach, the primary regulatory framework governing the protection of patient data in the United States was the Health Insurance Portability and Accountability Act (HIPAA). Enacted in 1996, HIPAA established national standards for protecting sensitive patient health information from being disclosed without the patient’s consent or knowledge. It includes the Privacy Rule, which sets standards for the protection of PHI, and the Security Rule, which specifies administrative, physical, and technical safeguards for electronic protected health information (ePHI).
While HIPAA has been instrumental in raising awareness and enforcing baseline security practices, its effectiveness in preventing sophisticated cyberattacks has been increasingly questioned. Critics argue that HIPAA’s prescriptive nature can be slow to adapt to rapidly evolving cyber threats. Furthermore, its enforcement mechanisms, while present, have not always deterred highly motivated and well-resourced attackers.
One significant limitation highlighted by the recent breach is the complexity of securing the supply chain. HIPAA mandates that Covered Entities (healthcare providers, plans, and clearinghouses) and their Business Associates (third-party vendors) protect PHI. However, the sheer number of vendors, sub-vendors, and interconnected systems creates a vast and often opaque network of potential vulnerabilities. A single weak link in this chain, as demonstrated by the 2026 incident, can compromise millions of records, even if the primary healthcare organization has robust internal defenses.
The 2026 healthcare data breach serves as a critical turning point, exposing the gaps in existing regulations and the urgent need for a more dynamic, comprehensive, and proactive approach to healthcare cybersecurity. The industry is now facing a reckoning, where the ‘old ways’ of compliance are no longer sufficient to safeguard patient data in the face of increasingly sophisticated cyber threats.
Anticipated New Regulations and Their Impact
In the wake of the 2026 healthcare data breach, policymakers and industry leaders are moving swiftly to develop and implement new regulations. While the exact details are still being finalized, several key areas are expected to be addressed:
1. Enhanced Supply Chain Security Mandates
One of the most significant changes will likely be a much stronger focus on supply chain cybersecurity. New regulations are expected to mandate more rigorous due diligence for third-party vendors, including regular security audits, penetration testing, and contractual obligations that hold vendors equally accountable for data breaches. Healthcare organizations may be required to maintain a comprehensive inventory of all third-party access points to PHI and implement real-time monitoring of vendor activities. This aims to close the vulnerability gap exploited in the recent breach.
2. Mandatory Advanced Threat Detection and Response
Beyond preventative measures, new regulations will likely emphasize proactive threat detection and rapid response capabilities. This could include mandates for advanced security technologies such as AI-driven threat intelligence, Security Information and Event Management (SIEM) systems with real-time analytics, and Endpoint Detection and Response (EDR) solutions. The goal is to reduce the dwell time of attackers within systems, minimizing the scope of potential data exfiltration.
3. Stricter Reporting Requirements and Penalties
Expect to see more stringent and accelerated breach notification requirements. The current HIPAA breach notification rules, while effective, may be deemed too slow in the context of large-scale, rapid data exfiltration. Fines and penalties for non-compliance are also expected to increase significantly, serving as a stronger deterrent and emphasizing the gravity of protecting patient data. There may also be provisions for individual liability for executives who fail to implement adequate security measures.
4. Investment in Cybersecurity Workforce Development
Recognizing the critical shortage of skilled cybersecurity professionals in healthcare, new initiatives may include funding and incentives for training and certification programs. Regulations might also encourage or mandate a certain level of cybersecurity expertise within healthcare organizations, perhaps requiring dedicated CISO (Chief Information Security Officer) roles with direct reporting lines to executive leadership.
5. Data Minimization and De-identification Standards
To reduce the impact of any future breaches, there may be a renewed push for data minimization – collecting and retaining only the necessary patient data – and enhanced standards for data de-identification and anonymization. This means that even if a breach occurs, the compromised data is less likely to be personally identifiable or exploitable.
These anticipated regulations are not merely cosmetic changes; they represent a fundamental shift towards a more resilient and secure healthcare cybersecurity posture. While compliance will undoubtedly present challenges for healthcare organizations, the long-term benefits in terms of patient trust and data integrity are immeasurable.
Best Practices for Healthcare Organizations in a Post-Breach World
In light of the 2026 healthcare data breach and the impending regulatory changes, healthcare organizations must proactively adapt their cybersecurity strategies. Here are some critical best practices:
- Comprehensive Risk Assessments: Regularly conduct thorough risk assessments to identify vulnerabilities across all systems, applications, and third-party integrations. This should include penetration testing and vulnerability scanning.
- Robust Access Controls: Implement strong access controls, including multi-factor authentication (MFA) for all users, especially those accessing sensitive patient data. Follow the principle of least privilege, ensuring users only have access to the information necessary for their role.
- Employee Training and Awareness: Human error remains a leading cause of data breaches. Regular, comprehensive cybersecurity training for all employees, focusing on phishing awareness, secure password practices, and reporting suspicious activities, is paramount.
- Incident Response Plan: Develop and regularly test a detailed incident response plan. This plan should outline clear steps for detection, containment, eradication, recovery, and post-incident analysis.
- Vendor Risk Management: Establish a stringent vendor risk management program. This includes thorough due diligence before engaging new vendors, contractual agreements that enforce security standards, and continuous monitoring of vendor compliance.
- Data Encryption: Encrypt all sensitive data, both in transit and at rest. This adds an extra layer of protection, making compromised data unreadable without the appropriate decryption keys.
- Regular Backups and Disaster Recovery: Implement a robust data backup and disaster recovery strategy to ensure business continuity and data availability in the event of a cyberattack or system failure.
- Patch Management: Maintain a rigorous patch management program to ensure all software and systems are up-to-date with the latest security patches, closing known vulnerabilities.
- Security Audits and Monitoring: Implement continuous security monitoring and conduct regular internal and external audits to ensure compliance with security policies and regulatory requirements.
By adopting these best practices, healthcare organizations can significantly reduce their risk exposure and build a more resilient defense against the ever-evolving threat landscape.
What Patients Can Do to Protect Themselves
While the onus is largely on healthcare organizations to secure data, patients also have a role to play in protecting their personal health information, especially after a major healthcare data breach. Here are actionable steps individuals can take:
- Monitor Your Explanations of Benefits (EOBs): Carefully review all EOBs from your insurance company for any services or prescriptions you did not receive. This can be an early indicator of medical identity theft.
- Check Your Credit Reports: Regularly obtain and review your credit reports from all three major credit bureaus (Equifax, Experian, and TransUnion). Look for any unfamiliar accounts or suspicious activity. You are entitled to a free report from each bureau annually.
- Set Up Fraud Alerts or Credit Freezes: Consider placing a fraud alert on your credit files, which requires creditors to verify your identity before extending new credit. For stronger protection, consider a credit freeze, which restricts access to your credit report.
- Be Wary of Phishing Attempts: After a data breach, cybercriminals often launch targeted phishing campaigns. Be extremely cautious of unsolicited emails, texts, or calls asking for personal or medical information. Always verify the sender’s legitimacy.
- Strong Passwords and MFA: Use strong, unique passwords for all your online accounts, especially those related to healthcare portals or insurance. Enable multi-factor authentication (MFA) wherever possible.
- Review Privacy Policies: Understand the privacy policies of your healthcare providers and insurance companies. Know how your data is collected, used, and shared.
- Report Suspicious Activity: If you suspect your medical identity has been stolen or if you notice any suspicious activity related to your healthcare accounts, report it immediately to your healthcare provider, insurance company, and potentially law enforcement.
Taking these proactive measures can significantly mitigate the risks associated with a healthcare data breach and empower patients to safeguard their sensitive information.
The Future of Healthcare Cybersecurity
The 2026 healthcare data breach serves as a critical inflection point for the industry. It has unequivocally demonstrated that the current cybersecurity paradigm is insufficient to protect sensitive patient data from increasingly sophisticated and persistent threats. The anticipated new regulations, while potentially burdensome in their implementation, are a necessary step towards building a more secure and trustworthy digital healthcare ecosystem.
The future of healthcare cybersecurity will likely be characterized by a multi-pronged approach: a combination of advanced technological solutions, robust regulatory frameworks, a highly skilled workforce, and a culture of security awareness at all levels. There will be a greater emphasis on proactive threat hunting, real-time monitoring, and collaborative intelligence sharing among healthcare organizations and government agencies.
Furthermore, the incident may accelerate the adoption of innovative security technologies such as zero-trust architectures, blockchain for secure data sharing, and even quantum-resistant cryptography in the long term. The goal is not just to react to breaches but to anticipate and prevent them, ensuring that the incredible benefits of digital healthcare are not overshadowed by the constant threat of cyberattacks.
Ultimately, the challenge is immense, but the stakes – the privacy, safety, and trust of millions of patients – are too high to ignore. The 2026 healthcare data breach must serve as a catalyst for fundamental and lasting change, forging a path towards a more secure and resilient future for healthcare data.