Navigating 2026 MedTech Cybersecurity Mandates: Preventing 70% of Data Breaches
The landscape of healthcare technology is evolving at an unprecedented pace, bringing with it incredible advancements in patient care. However, this progress is inextricably linked to increasing cybersecurity risks. As medical devices become more interconnected and sophisticated, so too does the potential for vulnerabilities that could compromise patient safety, data privacy, and operational integrity. The year 2026 marks a pivotal moment for the MedTech industry, with the introduction of stringent new cybersecurity mandates designed to bolster defenses against an ever-growing array of cyber threats. Understanding and proactively addressing these MedTech cybersecurity mandates is not just about compliance; it’s about safeguarding lives and preventing an estimated 70% of potential data breaches.
This comprehensive guide will delve into the intricacies of the upcoming 2026 MedTech cybersecurity mandates, exploring their origins, implications, and, most importantly, actionable strategies for manufacturers and healthcare providers to achieve robust security. We will dissect the core requirements, highlight common pitfalls, and provide a roadmap for building a resilient cybersecurity posture that goes beyond mere compliance, aiming for true protection.
The Urgency Behind New MedTech Cybersecurity Mandates
The healthcare sector has long been a prime target for cyber attackers due to the sensitive and valuable nature of patient data. Ransomware attacks, data breaches, and disruptions to essential medical services have become alarmingly frequent. These incidents not only incur massive financial costs but also erode public trust and, in critical cases, directly jeopardize patient outcomes. Traditional cybersecurity approaches, often reactive and fragmented, are proving insufficient against sophisticated, persistent threats.
Recognizing this escalating threat, regulatory bodies worldwide, including the U.S. Food and Drug Administration (FDA), have been pushing for more robust and proactive cybersecurity measures. The 2026 MedTech cybersecurity mandates are a direct response to this urgent need. They aim to shift the industry from a reactive stance to one of proactive risk management, embedding security into the entire lifecycle of medical devices, from design to decommissioning. These mandates are not merely an administrative burden; they are a critical investment in the future safety and reliability of healthcare technology.
The scope of these mandates is broad, encompassing everything from software bill of materials (SBOM) requirements to post-market surveillance and incident response planning. For organizations that fail to adapt, the consequences could be severe, ranging from regulatory penalties and product recalls to significant reputational damage and legal liabilities. More importantly, it leaves patients vulnerable. Therefore, understanding and implementing the 2026 MedTech cybersecurity mandates is paramount for every stakeholder in the healthcare ecosystem.
Key Pillars of the 2026 MedTech Cybersecurity Mandates
While specific details may vary slightly by region and regulatory body, the overarching principles of the 2026 MedTech cybersecurity mandates coalesce around several key pillars. These pillars form the foundation of a secure medical device ecosystem and dictate the responsibilities of manufacturers and, by extension, healthcare providers who utilize these devices.
1. Security by Design and Threat Modeling
One of the most significant shifts is the emphasis on ‘security by design.’ This means cybersecurity considerations must be integrated into the very initial stages of device conception and development, rather than being an afterthought. Manufacturers are expected to conduct thorough threat modeling exercises to identify potential vulnerabilities and attack vectors early in the design process. This proactive approach allows for the implementation of security controls that are intrinsic to the device’s architecture, making them far more effective and harder to bypass.
This pillar requires a fundamental change in development methodologies, fostering collaboration between engineering, cybersecurity, and regulatory teams from day one. It involves identifying critical assets, understanding potential threats, and designing countermeasures that mitigate risks before a product even reaches the market. For the 2026 MedTech cybersecurity mandates, security is no longer an add-on but a core functional requirement.
2. Software Bill of Materials (SBOM) Requirements
The mandate for a comprehensive Software Bill of Materials (SBOM) is a game-changer. An SBOM is essentially a complete, nested inventory of all software components, libraries, and dependencies used in a medical device. This transparency is crucial for several reasons:
- Vulnerability Management: It allows manufacturers and users to quickly identify if a newly discovered vulnerability (e.g., in an open-source library) affects their device.
- Supply Chain Security: It provides visibility into the software supply chain, helping to assess risks associated with third-party components.
- Incident Response: In the event of a breach, an SBOM accelerates the identification of affected components and the deployment of patches.
Generating and maintaining accurate SBOMs throughout the device lifecycle will be a significant undertaking but is central to meeting the 2026 MedTech cybersecurity mandates. This requirement alone can dramatically improve the ability to track and remediate vulnerabilities, preventing a substantial percentage of data breaches.
3. Vulnerability Management and Patching
The mandates will necessitate robust processes for identifying, assessing, and remediating cybersecurity vulnerabilities post-market. This includes continuous monitoring for new threats, timely issuance of patches and updates, and clear communication channels with healthcare providers regarding security advisories. Manufacturers must demonstrate a defined plan for vulnerability disclosure and resolution, ensuring that devices remain secure throughout their operational lifespan.
Effective vulnerability management is a continuous cycle, not a one-time event. It requires dedicated resources, a clear methodology, and a commitment to rapid response. For the 2026 MedTech cybersecurity mandates, simply releasing a device and hoping for the best is no longer an option.
4. Incident Response and Recovery Planning
No system is entirely impervious to attack. Therefore, the mandates emphasize the critical importance of having a well-defined and tested incident response plan. This plan should detail procedures for detecting, containing, eradicating, and recovering from cybersecurity incidents. It must also include provisions for reporting incidents to relevant authorities and communicating effectively with affected parties.
A strong incident response capability minimizes the damage from a breach and accelerates recovery, significantly contributing to preventing a larger data compromise. Regular drills and simulations are vital to ensure that these plans are effective and that personnel are prepared to act swiftly when an incident occurs. This proactive preparation is a cornerstone of the 2026 MedTech cybersecurity mandates.
5. Secure Software Development Lifecycle (SSDLC)
Manufacturers will be required to implement a Secure Software Development Lifecycle (SSDLC) that embeds security activities into every phase of software development, from requirements gathering to testing and deployment. This includes practices like secure coding guidelines, static and dynamic application security testing (SAST/DAST), penetration testing, and code reviews. The goal is to minimize security flaws introduced during development, reducing the attack surface of medical devices.
Strategies to Prevent 70% of Data Breaches Under New Mandates
Achieving compliance with the 2026 MedTech cybersecurity mandates is not just about ticking boxes; it’s about fundamentally transforming how medical devices are secured. By strategically implementing robust cybersecurity practices, organizations can realistically aim to prevent a significant majority of data breaches. Here are actionable strategies:
1. Establish a Dedicated Cybersecurity Governance Framework
Effective cybersecurity begins with strong governance. Establish a clear framework that defines roles, responsibilities, policies, and procedures for cybersecurity across the organization. This includes:
- Cross-functional Team: Create a dedicated team comprising cybersecurity experts, product developers, regulatory affairs, and legal personnel.
- Regular Audits and Assessments: Conduct periodic internal and external audits to assess compliance and identify areas for improvement.
- Leadership Buy-in: Ensure top-level management understands and champions cybersecurity initiatives, allocating necessary resources.
A well-defined governance structure ensures that cybersecurity is not an isolated function but an integrated part of the business strategy, critical for navigating the 2026 MedTech cybersecurity mandates.
2. Implement Comprehensive Risk Management Methodologies
Beyond basic threat modeling, adopt a comprehensive, continuous risk management program. This involves:
- Asset Inventory: Maintain an up-to-date inventory of all medical devices, software, and associated data assets.
- Risk Assessment: Regularly assess the likelihood and impact of potential cyber threats to these assets.
- Mitigation Strategies: Develop and implement specific mitigation strategies for identified risks, prioritizing those with the highest impact and likelihood.
- Residual Risk Acceptance: Clearly document and formally accept any residual risks that cannot be fully mitigated.
This proactive approach allows organizations to focus resources where they are most needed, significantly reducing overall risk exposure in line with the 2026 MedTech cybersecurity mandates.
3. Fortify Your Software Supply Chain Security
The increasing reliance on third-party software components and cloud services introduces supply chain vulnerabilities. To address this:
- Vendor Due Diligence: Thoroughly vet all third-party vendors and suppliers for their cybersecurity practices.
- Contractual Agreements: Incorporate strong cybersecurity clauses in all vendor contracts, explicitly outlining security requirements and responsibilities.
- Continuous Monitoring: Monitor third-party components (via SBOMs) for newly disclosed vulnerabilities and ensure prompt patching.
A compromised supply chain can lead to widespread breaches, making this a critical area of focus for the 2026 MedTech cybersecurity mandates.
4. Invest in Advanced Threat Detection and Monitoring
Passive security measures are no longer enough. Implement advanced threat detection and continuous monitoring solutions that can identify suspicious activities in real-time. This includes:
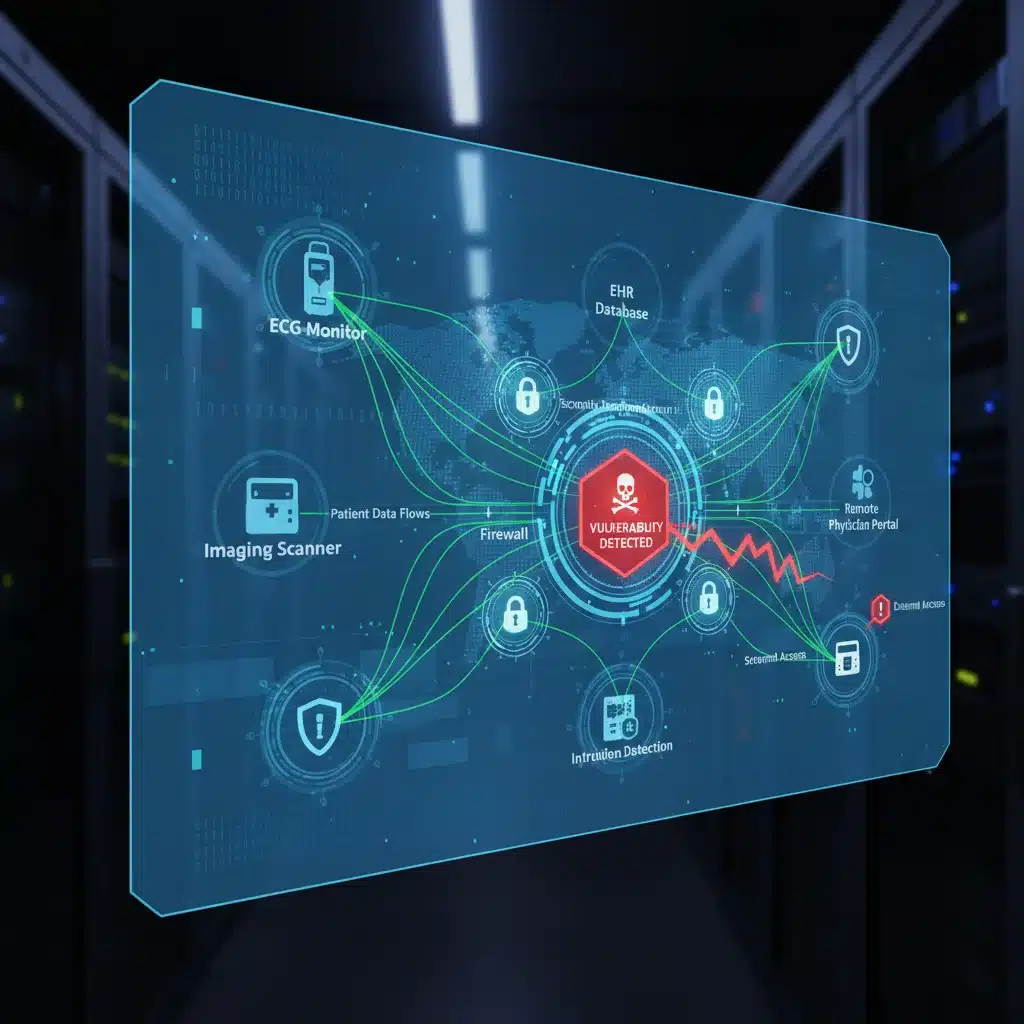
- Security Information and Event Management (SIEM): Centralize and analyze security logs from all devices and systems.
- Intrusion Detection/Prevention Systems (IDS/IPS): Monitor network traffic for malicious activity and block known threats.
- Endpoint Detection and Response (EDR): Provide advanced threat detection and response capabilities on individual medical devices and workstations.
Early detection is key to containing breaches before they escalate, directly contributing to the goal of preventing 70% of data breaches under the 2026 MedTech cybersecurity mandates.
5. Prioritize Secure Authentication and Access Control
Weak authentication and unauthorized access are common entry points for attackers. Implement strong access control measures:
- Multi-Factor Authentication (MFA): Mandate MFA for all access to sensitive systems and data.
- Least Privilege Principle: Grant users and devices only the minimum necessary access required to perform their functions.
- Regular Access Reviews: Periodically review and revoke unnecessary access privileges.
- Strong Password Policies: Enforce complex password requirements and regular password changes.
These fundamental security practices are non-negotiable for compliance with the 2026 MedTech cybersecurity mandates and for preventing unauthorized data access.
6. Implement Data Encryption and Data Loss Prevention (DLP)
Protecting data at rest and in transit is paramount. Utilize robust encryption methods for sensitive patient data stored on devices, servers, and transmitted across networks. Additionally, implement Data Loss Prevention (DLP) solutions to prevent unauthorized transfer or leakage of sensitive information outside the controlled environment. DLP tools can monitor, detect, and block sensitive data from leaving the organization’s network, significantly reducing the risk of accidental or malicious data breaches. This is a critical component of adhering to the 2026 MedTech cybersecurity mandates.
7. Conduct Regular Security Training and Awareness Programs
Human error remains a leading cause of data breaches. Invest in continuous security awareness training for all employees, from engineers to clinical staff. Topics should include phishing awareness, secure handling of patient data, identifying suspicious activities, and understanding their role in maintaining cybersecurity. A well-informed workforce is your strongest defense against social engineering attacks and accidental data exposure, directly supporting the objectives of the 2026 MedTech cybersecurity mandates.
8. Embrace Collaboration and Information Sharing
The cybersecurity threat landscape is constantly evolving. No single organization can tackle it alone. Foster collaboration with industry peers, regulatory bodies, and cybersecurity intelligence sharing organizations (e.g., ISACs). Sharing threat intelligence, best practices, and lessons learned from incidents can significantly strengthen the collective defense of the MedTech sector. This collaborative spirit is increasingly encouraged by the 2026 MedTech cybersecurity mandates, recognizing that shared knowledge leads to shared security.
Challenges and Overcoming Them
While the 2026 MedTech cybersecurity mandates are essential, implementing them presents several challenges:
- Legacy Devices: Integrating new security features into older, deployed devices can be complex and costly. Manufacturers must develop strategies for securing legacy products, potentially involving network segmentation or virtual patching.
- Resource Constraints: Small to medium-sized MedTech companies may struggle with the financial and human resources required for comprehensive cybersecurity programs. Collaboration, shared services, and leveraging specialized cybersecurity partners can help mitigate this.
- Evolving Threat Landscape: Cyber threats are dynamic. Compliance is not a static state but an ongoing process of adaptation and improvement.
- Interoperability vs. Security: Balancing the need for seamless device interoperability with robust security measures requires careful design and implementation.
Overcoming these challenges requires strategic planning, a commitment to continuous improvement, and a willingness to invest in the necessary infrastructure and expertise. The long-term benefits of enhanced security, reduced breach risks, and continued market access far outweigh the initial investment.
The Role of Healthcare Providers
While manufacturers bear the primary responsibility for designing secure devices, healthcare providers play an equally critical role in ensuring their secure deployment and operation. Healthcare organizations must:
- Conduct Device Inventory and Risk Assessment: Understand what medical devices are on their network, their vulnerabilities, and their potential impact.
- Implement Network Segmentation: Isolate medical devices from general IT networks to limit the spread of potential breaches.
- Apply Patches and Updates: Work closely with manufacturers to apply security patches and updates in a timely manner.
- Secure Device Configuration: Ensure devices are configured securely, changing default passwords and disabling unnecessary services.
- Monitor Device Activity: Implement monitoring solutions to detect unusual or malicious activity on medical devices.
- Staff Training: Educate clinical and IT staff on secure device usage and cybersecurity best practices.
The 2026 MedTech cybersecurity mandates create a shared responsibility model, where the security of patient care depends on the collaborative efforts of both device manufacturers and the healthcare facilities that use them.
Conclusion: A Secure Future for MedTech
The 2026 MedTech cybersecurity mandates represent a crucial turning point for the medical technology industry. They are not merely regulatory hurdles but a vital framework for building a more resilient, trustworthy, and ultimately safer healthcare ecosystem. By embracing security by design, implementing comprehensive risk management, fortifying the supply chain, and fostering a culture of cybersecurity awareness, organizations can move beyond basic compliance.
The goal of preventing 70% of data breaches is ambitious but achievable with a concerted, proactive effort. Manufacturers and healthcare providers who view these mandates as an opportunity to innovate and strengthen their security posture will not only avoid penalties but also enhance their reputation, protect patient data, and contribute to a more secure future for medical innovation. The time to act is now, preparing diligently for the 2026 MedTech cybersecurity mandates to ensure that technological advancements continue to serve humanity without compromising safety or privacy.